RiskOps
RiskOps — BT ve siber güvenlik risk yönetimi platformu

IT & CYBER RISK MANAGEMENT

RiskOps

Risk register · 5×5 assessment · action tracking

8PHPStan level
192tests
0dependencies
2languages
Browse the running app → Source code

The demo is real output captured from the running app — not screenshots. Navigation works; saving and filtering do not.
WHAT IT IS

A risk is not closed — its level is lowered

RiskOps was written to record an organisation's IT and cyber security risks, score them by likelihood × impact, track mitigating actions and produce documents that can be handed to management.

Risk lifecycle: record, assessment, severity, action plan, reassessment

Register

Automatic risk codes, 5×5 matrix, soft delete. The score is a generated column — the application never computes it, so it cannot drift.

Actions

Mitigating actions linked to a risk, with an owner and a due date. Overdue actions are flagged on the dashboard and in reports.

Reports

Six built-in reports and a one-page Executive Summary: letterhead, confidentiality notice and a signature block, ready to print.

SCOPE

What RiskOps is not

This distinction is the most important design decision, so it is stated up front.

Not thisWhy it matters
Helpdesk / ticketing There is no “request to close” here — there is an ongoing risk state.
ITSM tool Asset inventory, change management and SLA tracking are out of scope.
Vulnerability scanner It does not scan; it is where scan results are managed.
SIEM It does not collect logs or correlate events.

SCREENS

Browse the real application

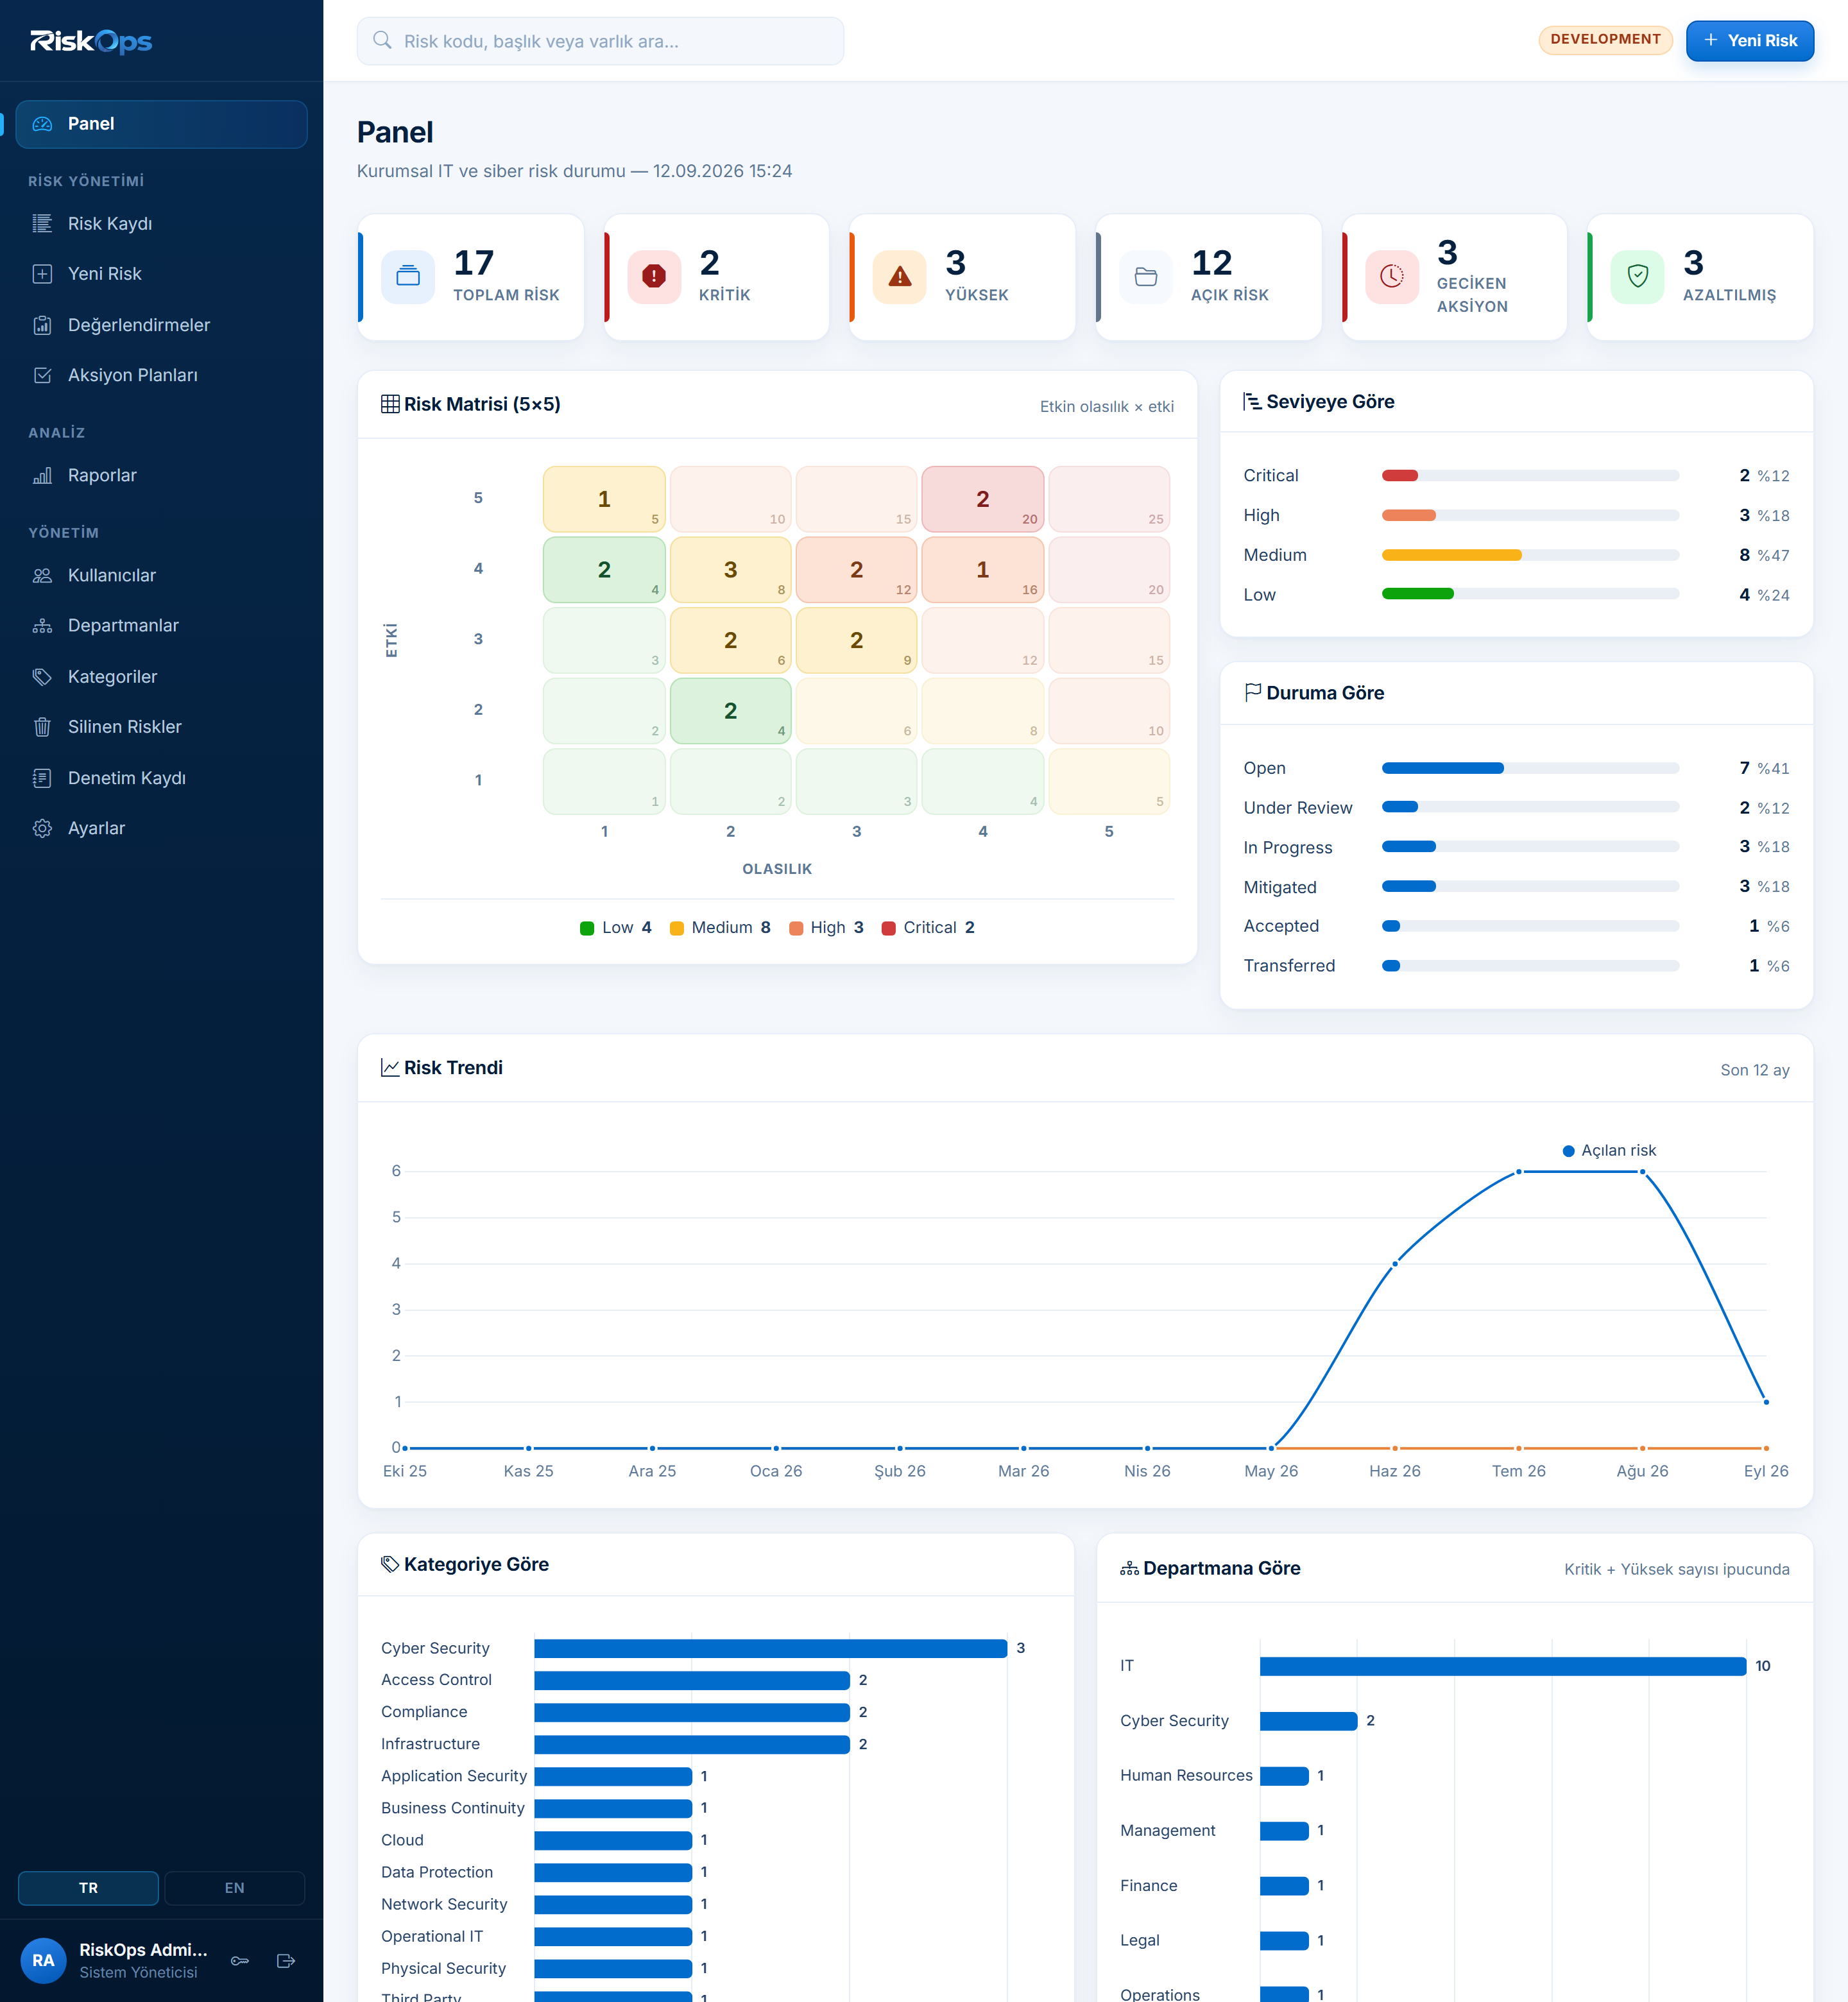
Each image opens that screen in the demo. The demo is HTML captured from a running installation: same CSS, same data, same layout.

RiskOps dashboard
Dashboard matrix · trend · distributions
Risk detail screen
Risk detail assessment history · actions
Executive summary report
Executive Summary one page · print ready
Plugin administration screen
Plugins hooks · no sandbox

QUALITY

Measured, not claimed

These numbers come from tools in the repository and are re-measured by CI on every push.

8PHPStan level, no baseline
192unit + integration tests
0runtime dependencies
12architecture decision records

Security defaults

  • Passwords via password_hash(), CSRF on every POST
  • Authorisation is server-side; the UI only hides things
  • Deletion requires POST + CSRF + permission
  • No unsafe-inline in CSP — no inline scripts

Decisions are written down

Why there is no framework, why the translation key is the Turkish source string, why no sandbox is claimed for plugins — each with its reasoning in the ADRs.

INSTALL

Two commands

With Docker

git clone https://github.com/CodeByPinar/riskops.git
cd riskops && docker compose up

Then open localhost:8080. Demo data is optional and loads with a single command.

Without Docker

Ubuntu 24.04 · PHP 8.3 · MariaDB 10.11 · Apache 2.4. The schema is a single file and can be loaded twice (idempotent). Steps are in the README.